Cloudflare's Free Security Audit Skill for Claude Code
TL;DR
Cloudflare open sourced a free skill that turns Claude Code into a security auditor. It maps your app, sends a team of AI agents to hunt for bugs, has a separate agent try to disprove each one, and gives you a report of the verified issues with fixes.
👉 https://www.skool.com/claudecodeclub
Find security holes in your app with Cloudflare's free skill
security-audit-skill is a free, open source skill from Cloudflare (MIT license, about 28,000 GitHub stars). It seeded the harness Cloudflare uses to find vulnerabilities in its own code. You add it to a coding agent like Claude Code, and the agent audits your codebase for security problems.
Run security-audit-skill on your own codebase
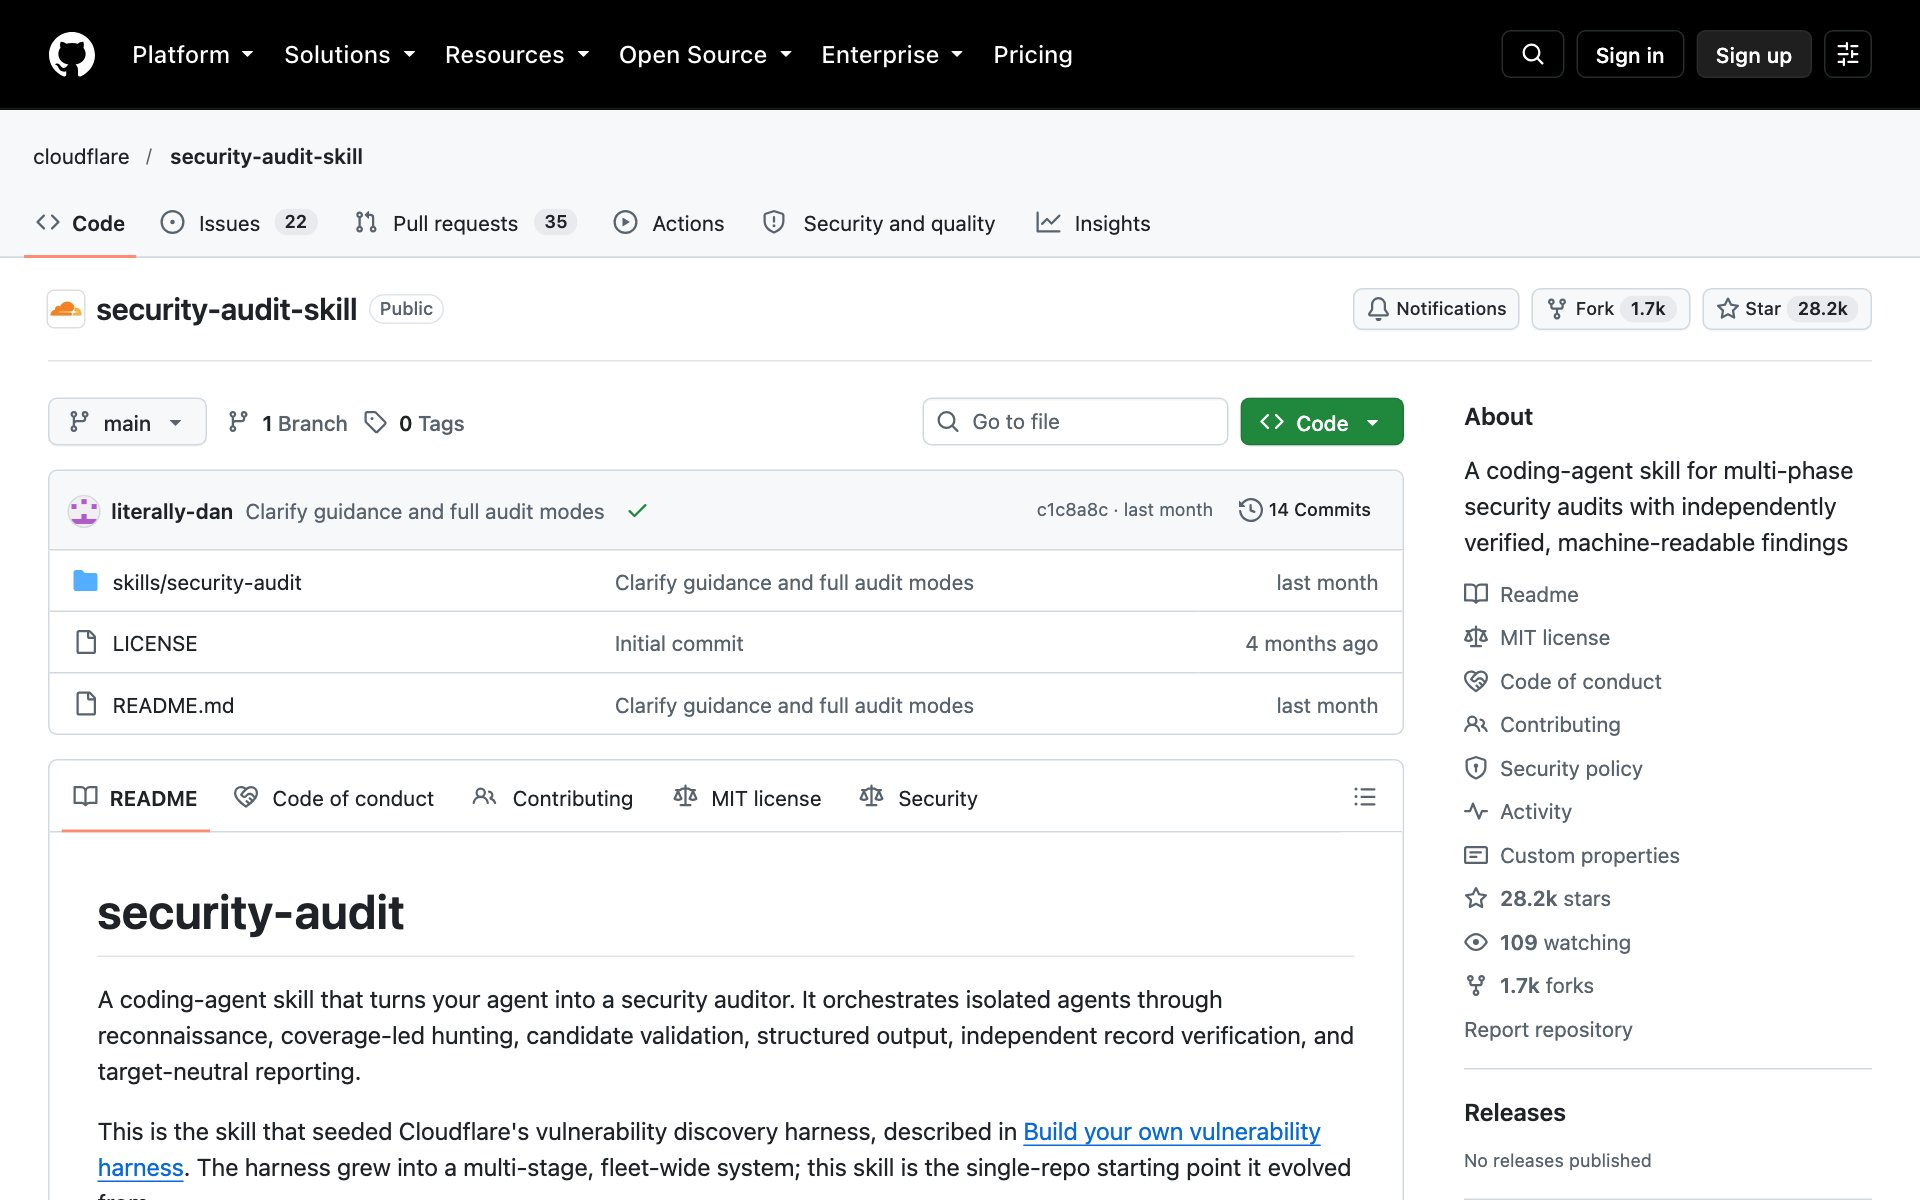
What security-audit-skill does for you: it runs a six phase audit. First it maps your app: how it is built, where untrusted input comes in and what it trusts. Then a team of separate agents hunts through the code for bugs, such as holes in logins, your database and your APIs, and prompt injection if your app uses AI. Every bug it finds goes to a fresh agent whose only job is to disprove it. Only the bugs that survive land in the report, each one with how to fix it.
How to install security-audit-skill: copy the repo URL below, paste it into Claude Code, and say: install this.
repo URLhttps://github.com/cloudflare/security-audit-skillOr install it by hand with the Skills CLI (you need Node.js):
bashnpx skills add https://github.com/cloudflare/security-audit-skill --skill security-auditBest practices for security-audit-skill:
- Start Claude Code inside the project folder you want audited, so the skill reads the right code.
- Run the audit more than once. Cloudflare says one run found roughly half of what repeated runs found in total, and each new run builds on the last one.
- Read the needs_validation list too. Those are leads the agents could not prove or disprove, and they are worth a human look.
- Run it inside a sandbox when your project builds or runs code. The skill asks for one so it never runs untrusted code on your real machine.
Prompts to try with security-audit-skill:
promptsecurity audit this codebasepromptfind security vulnerabilities in ./src and explain how to fix each one in plain EnglishWhere to start with security-audit-skill
- Pick one project you already shipped, like a vibe coded app with logins and a database, and audit that first.
- Fix the confirmed issues first, then the needs_validation ones, then run the audit again.
👉 https://www.skool.com/claudecodeclub
Common questions
Is Cloudflare's security audit skill free?
Yes. security-audit-skill is open source under the MIT license, so you can use it for free.
How do I install security-audit-skill?
Paste the repo URL into Claude Code and say: install this. Or run npx skills add with the repo URL and --skill security-audit.
How does security-audit-skill avoid false alarms?
Every bug candidate goes to a fresh agent whose job is to disprove it. Bugs that cannot be proven are kept as needs_validation, and disproved ones are marked rejected.
What do I get at the end of an audit?
A report of the verified issues, a detailed findings file and a list of leads that still need a human check. The skill saves them in a folder you choose, or in a default folder in your home directory.
Keep going
Want to build with Claude Code, not just learn about it?
Get 650+ plug-and-play skills, MCPs & prompts, plus 8,000+ members - $9/mo, cancel anytime.
Join the Club