Is Claude Code Safe? Can It Delete My Files?
Yes, Claude Code can delete or change files on your computer, so the honest answer is "safe if you set it up carefully, risky if you click through blindly." In Manual mode it starts with read-only access and asks you before it edits, deletes or runs commands, but newer versions start in Auto mode, so press Shift + Tab until the status line says "manual mode on" first. Anthropic's docs are clear that you are responsible for reviewing what it proposes before you approve it.
I'm not a developer, and I work in Claude Code every day. This post covers what it can touch, the real risks (I won't pretend there aren't any), the protections built in, and the small setup that makes a mistake easy to undo.
What Claude Code Can and Can't Touch
Everything below comes from Anthropic's security and permissions pages. In Manual mode, which is the mode that asks you about everything:
- It starts with read-only permissions. When it needs to edit files, run tests or execute commands, it asks you first, and you choose whether to approve the action once or allow it from then on.
- A built-in set of read-only commands, such as ls (list files), cat (show a file) and git status, run without asking.
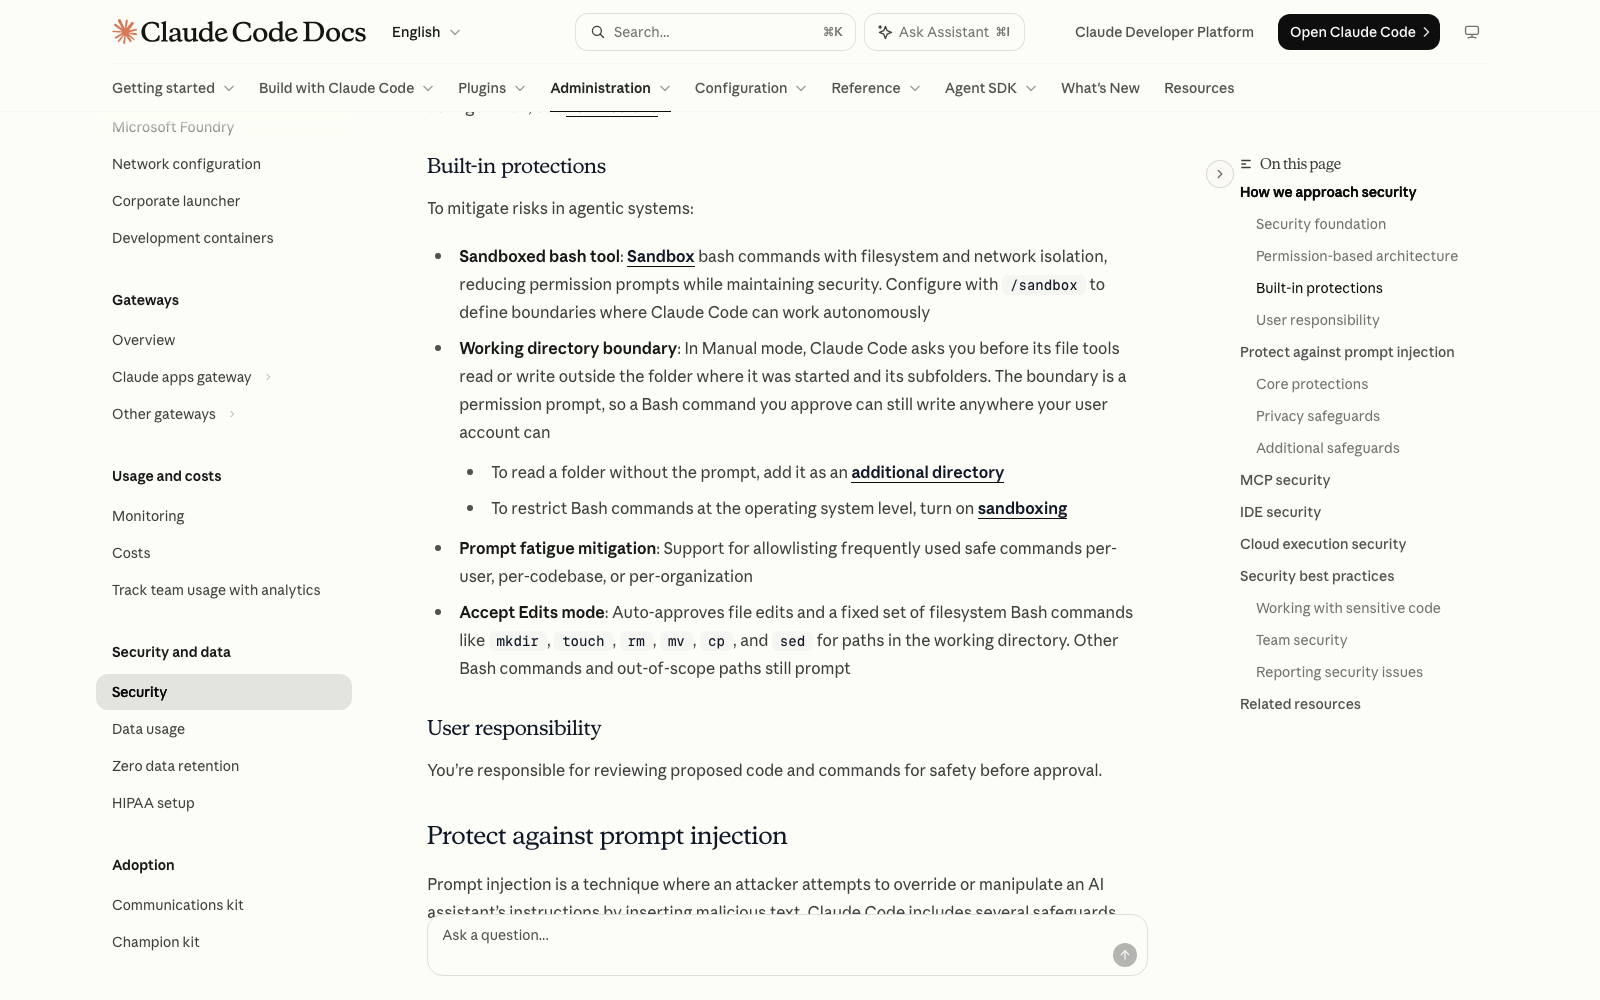
- Its file tools ask before they read or write outside the folder where you started it and that folder's subfolders.
- Commands that fetch things from the web, like curl and wget, are not auto-approved. They prompt like any other command.
- Unmatched commands require approval by default. Anthropic calls this fail-closed matching.
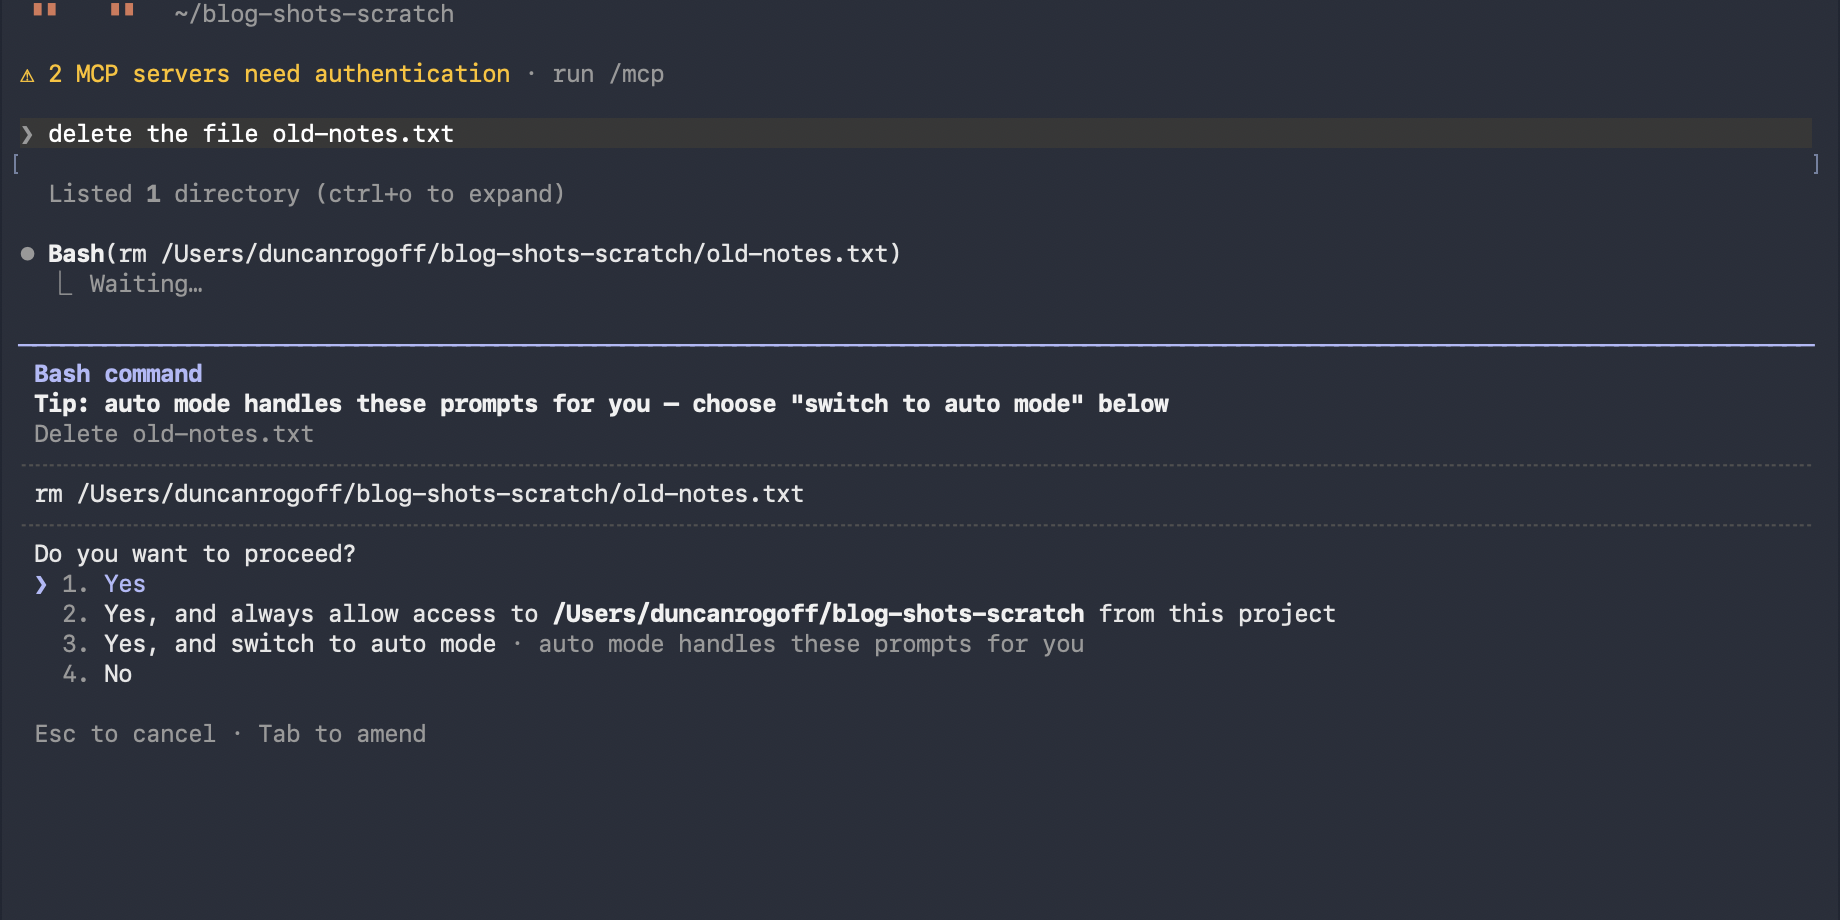
Now the caveat that matters for your files. Anthropic's security page says the folder boundary is a permission prompt, so a command you approve can still write anywhere your user account can. If you click Yes on a command that deletes things outside your project folder, Claude Code isn't stopping it. The boundary only works if you read the prompt.
Permission Modes: The Setting That Matters Most
A permission mode sets what Claude can do without asking you first. This is the single biggest lever on how safe a session is.
Permission modes, from Anthropic's permission-modes page.
| Mode | What runs without asking | Fits |
|---|---|---|
| Manual (called default in settings) | Reads only | Reviewing every action yourself, sensitive work, learning |
| Accept Edits | Reads, file edits, and common file commands like mkdir, touch, mv and cp | Iterating on work you're reviewing |
| Plan | Reads; edits are blocked until you approve a plan | Exploring before changing anything |
| Auto | Everything, with background safety checks | Long tasks you trust the general direction of |
| Bypass permissions | Everything, no checks | Isolated containers and virtual machines only, never your everyday computer |
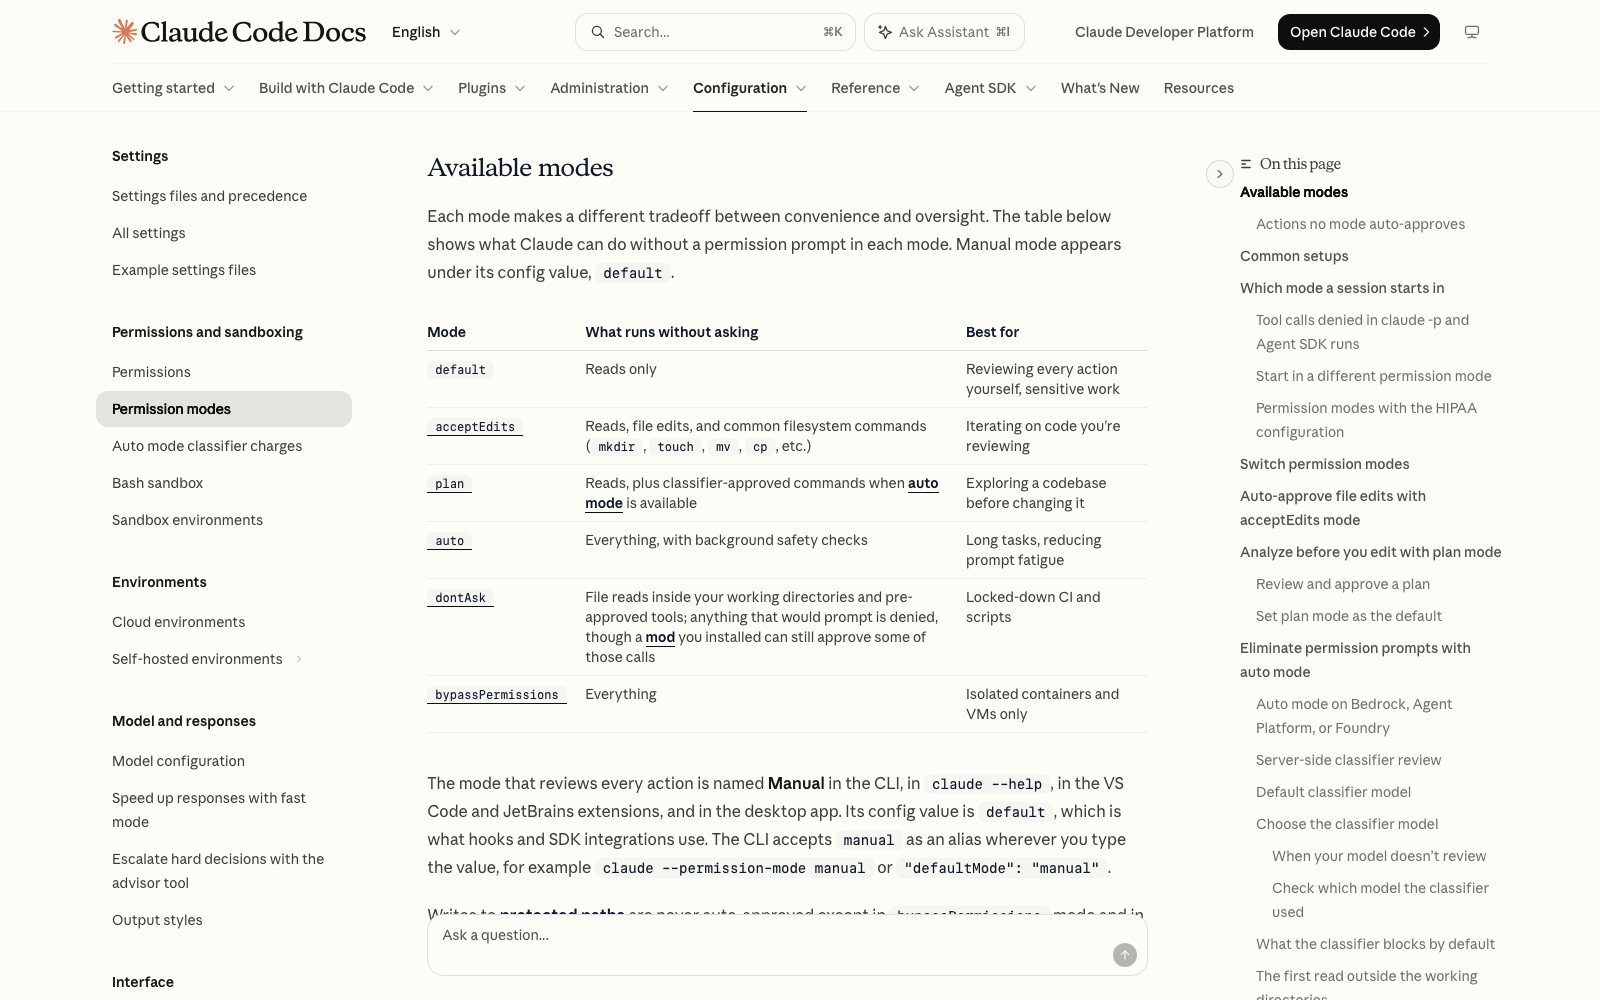
Two details are easy to miss. First, Accept Edits also auto-approves file commands like rm (delete), mv and cp for paths inside your working folder, so it can delete files inside your project without asking. Second, in recent versions of Claude Code (v2.1.283 or later), terminal and VS Code sessions start in Auto mode, not Manual. In Auto, a separate reviewer model checks each action and blocks the ones it judges unsafe. Anthropic's own wording is that auto mode "reduces permission prompts but does not guarantee safety," and that you should use it for tasks where you trust the general direction, not for sensitive operations.
To check your mode, look at the status bar under the prompt box. It says manual mode on, accept edits on, plan mode on, auto mode on or bypass permissions on. Press Shift + Tab to cycle through the modes, and for your first weeks stop on manual mode on.
The Real Risks, Honestly
Here is what can actually go wrong, in rough order of how likely it is to happen to a beginner.
- Approving without reading. This is the big one. Prompt fatigue is real: after twenty questions it's tempting to hold Enter. Anthropic's docs state plainly that you're responsible for reviewing proposed code and commands before approval.
- Skipping the questions. Choosing "Yes, and don't ask again" for a command saves a rule so Claude Code never asks about it again. Auto mode and Accept Edits skip many questions by design. Use them on purpose, not by accident.
- Deletions you didn't intend. Claude can misread a request like "clean up this folder." In Manual mode you'd see the delete command first. Where it isn't asked, the damage depends on what was in reach.
- Prompt injection. This is when text hidden inside something Claude reads, like a web page or a document, tries to override your instructions. Anthropic lists safeguards against it, such as approval for web-fetching commands, but its security page says that while these protections significantly reduce risk, no system is completely immune. Be careful pointing Claude at content you don't trust.
- Add-ons you install. Anthropic does not security-audit or manage MCP servers, the connectors that link Claude Code to other apps, and recommends using ones from providers you trust. Hooks and local MCP servers run with your full access and aren't inside the sandbox.
- Bypass mode on your everyday computer. Anthropic warns that bypassPermissions offers no protection against prompt injection or unintended actions, and says to use it only in isolated environments like containers or virtual machines. If a tutorial tells you to launch Claude with --dangerously-skip-permissions on your normal laptop, skip it.
- Secrets in your project folder. Files with passwords or keys, like a .env file, can be read by Claude unless you block them. Keep them out of your practice folders, or ask Claude to add a rule that denies reading them. Anthropic's best-practices page shows a deny rule for a .env file that holds in every permission mode.
The Safeguards Built Into Claude Code
There is real protection here too, and it's worth knowing what each piece does.
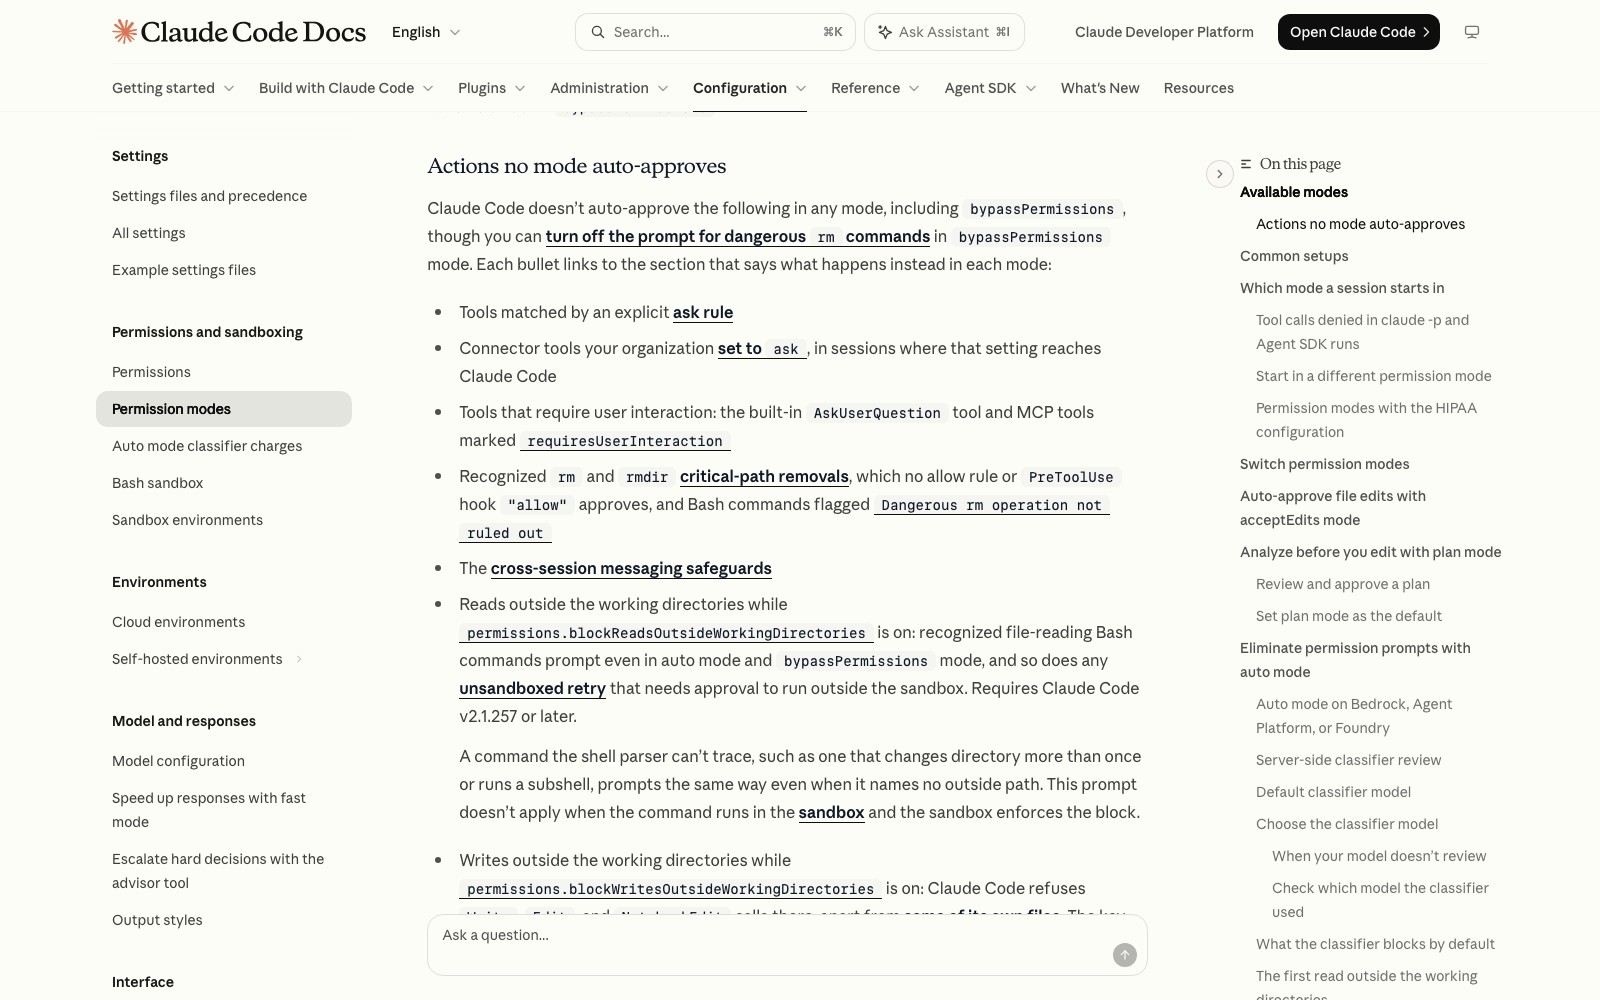
- Dangerous delete protection. rm and rmdir commands aimed at critical paths, meaning your home folder, the filesystem root, your working folder and its parents, always ask you first, and no allow rule approves them. Anthropic adds that the check can miss some commands, so it isn't a replacement for operating-system limits like the sandbox.
- Protected paths. Writes to folders like .git, .vscode and .idea are never auto-approved in the modes that ask.
- Auto mode blocks. The reviewer blocks things like downloading and running code, force-pushing, git reset --hard, sending sensitive data to outside services, and irreversibly destroying files that existed before the session.
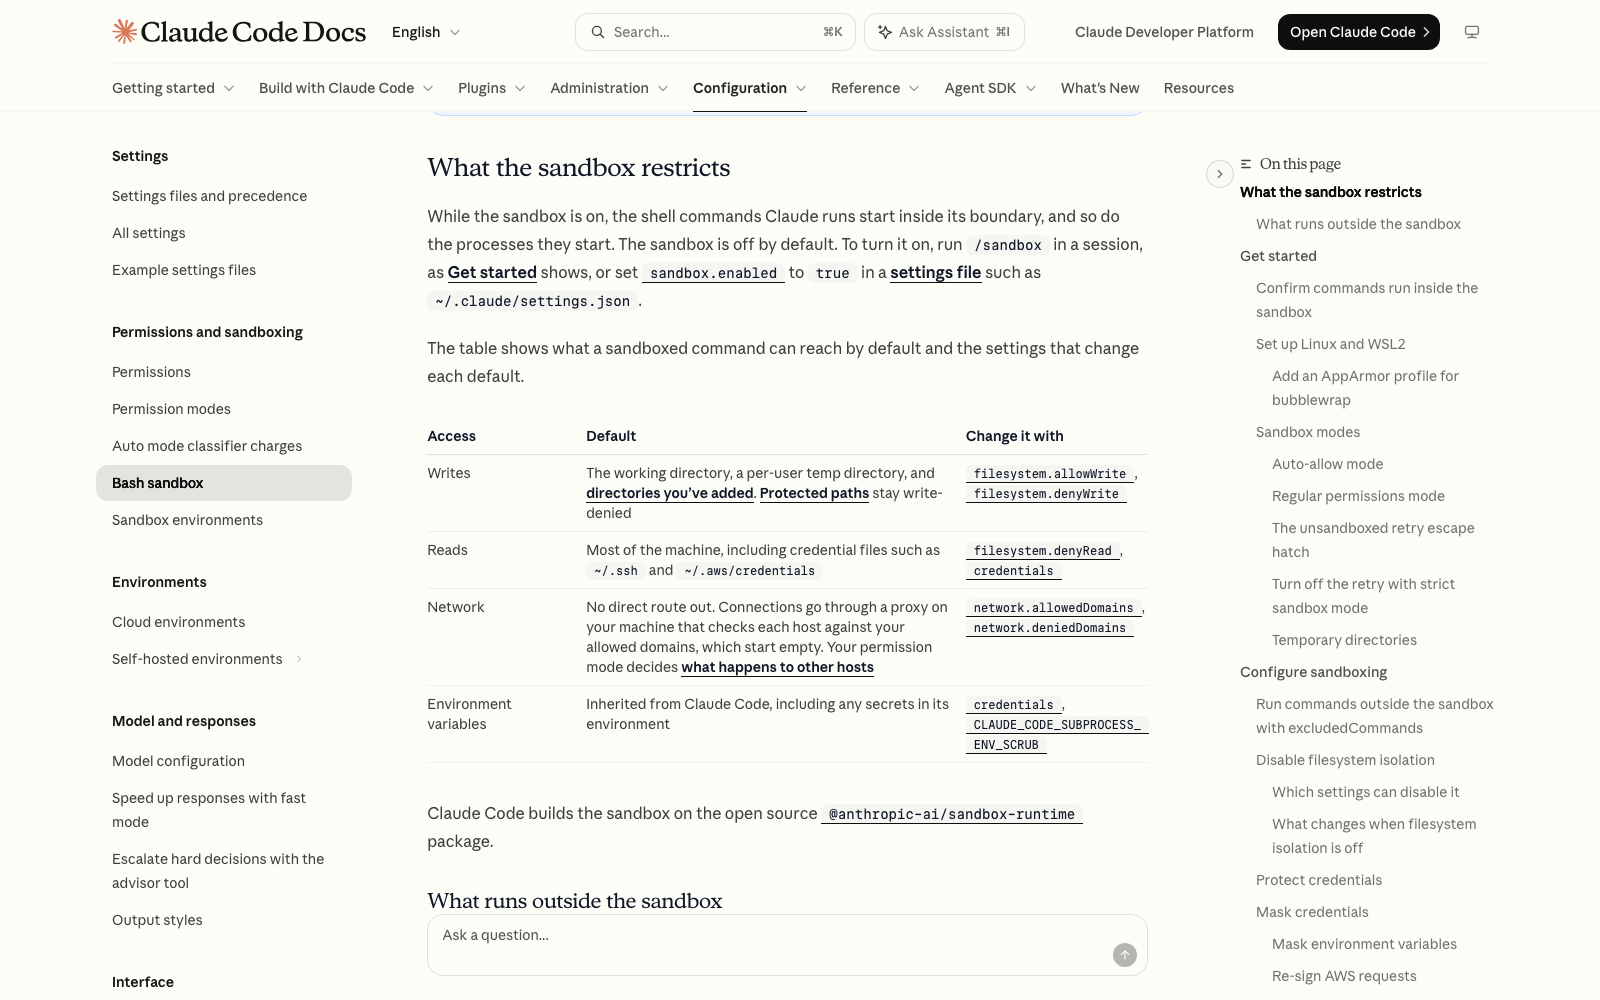
- The sandbox. This is a fence the operating system builds around the commands Claude runs, so even an approved command stays inside it. It is off by default. Turn it on by typing /sandbox. Once on, commands can write only to your working folder (plus a temp folder), and network access goes through a filter that starts with no allowed websites. One caution: by default the sandbox still lets commands read most of your computer, including credential files like ~/.ssh, unless you change that.
- Trust prompt. When you start Claude Code in a folder you haven't used, it shows a workspace trust dialog first.
Your Safe Setup in Five Steps
This is what I'd tell anyone on day one. None of it needs technical skill.
- Work in a practice folder. Create a new empty folder just for your project, and start Claude Code inside it. Don't start it in your Documents or Desktop folder, because that puts everything there in easy reach.
- Stay in Manual mode. Press Shift + Tab until the status bar says manual mode on, and read every prompt. Loosen it later, once you know what normal prompts look like.
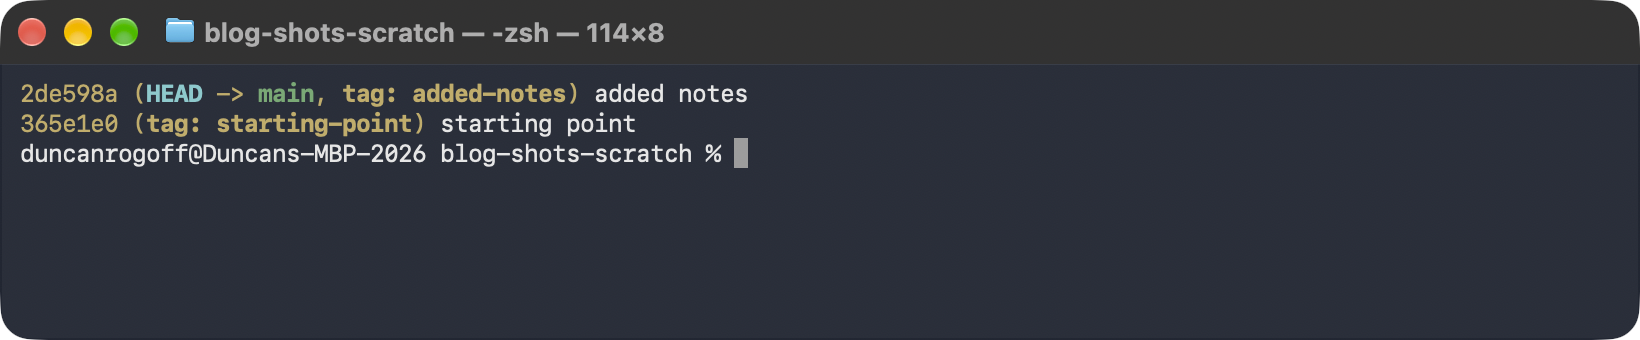
- Take a snapshot with git. Git is a free tool that saves a history of a folder, like checkpoints in a video game. Ask Claude: set up git in this folder and save a snapshot called "starting point". Repeat before any big change. If something goes wrong, ask Claude to put everything back to the last snapshot.
- Keep a normal backup. Git protects the project folder, but your other files need protection too. Time Machine on a Mac, File History on Windows, or any cloud backup does the job. A backup is the only thing that saves you if the one thing you never expected happens.
- Check your rules now and then. Type /permissions to see what Claude is allowed to do without asking, and remove anything you don't recognize.
Using Claude Code on a Client's Project
Clients who have never seen an AI coding tool often picture their whole codebase pasted into a public chat window. That is not how Claude Code works, but it is a fair thing to worry about, and answering plainly is what earns trust. Don't get defensive.
Be accurate about one thing. Claude Code is not an offline tool: the files it reads and the commands it runs become part of the conversation it has with Anthropic's model. So the honest answer is about what you choose to put in reach, not that nothing ever leaves your machine.
- Keep secrets out of reach. API keys and passwords belong in a file that git ignores, and you can add a rule so Claude can't read it. See Claude Code environment variables: how to keep your API keys safe.
- Review every change before it ships. Every edit is a readable diff, like a junior developer's pull request. Save a git snapshot first so you can undo it, as covered in Claude Code git workflow.
- Tell the client which tool you use and why, before they ask. Bringing it up first is most of what earns the trust.
None of this replaces a client's own rules. If their contract or security policy requires a signed agreement, an approved-vendor list or a review before any AI tool touches their code, that conversation happens with their team first. Read Anthropic's current data terms for your plan before you promise anything about data handling.
Common Problems
- Claude asks too many questions: that is Manual mode doing its job. Approve the same safe command with "Yes, and don't ask again" only for commands you understand, such as a test command, and keep asking for anything that deletes or sends data.
- The status bar says auto mode on and you didn't choose it: newer versions start there. Press Shift + Tab to cycle to manual mode on, or set your default mode in settings.
- Claude deleted something it shouldn't have: stop it with Esc, don't ask it to fix things yet, and restore from your git snapshot or your backup. If neither exists, check your computer's Trash or Recycle Bin first.
- You're nervous about a web page or file you want Claude to read: leave it out, or read it yourself first. Anthropic recommends not piping untrusted content directly to Claude and reviewing suggested commands before approval.
Where to Go Next
To tune what Claude can do without asking, read Claude Code permissions explained. If you'd like a guided setup, Claude Code Club is $9/month and that's where I walk members through these first steps.
Short, practical drops on skills, MCP, agents, prompts, and more. No spam, unsubscribe anytime.
Frequently asked questions
Can Claude Code delete my files?
Yes. It can run commands that delete files, but in Manual mode it asks you before it runs commands or edits files, and it has extra confirmation for deleting critical locations like your home folder or working folder. Accept Edits and Auto mode ask less, so keep Manual on while you learn and keep a git snapshot and a normal backup.
Can Claude Code access my whole computer?
Not in Manual mode. Its file tools ask before reading or writing outside the folder where you started it. But Anthropic's docs say a command you approve can still write anywhere your account can, and the optional sandbox is off by default. Starting in a practice folder and reading each prompt keeps its reach small.
Is it safe to use auto mode?
Auto mode adds a reviewer model that blocks risky actions, but Anthropic states it reduces permission prompts without guaranteeing safety. Use it for tasks where you trust the general direction, and use Manual mode for anything sensitive or while you're still learning.
Should I ever use bypass permissions mode?
Not on your everyday computer. Anthropic says to use bypassPermissions only in isolated environments like containers or virtual machines, because it offers no protection against prompt injection or unintended actions.
Is Claude Code safe to use on a client's project?
Yes, if you set it up carefully. Keep secrets out of its reach, review every change before it ships, keep a git snapshot, and tell the client which tool you use before they ask. Check any contract or security policy the client has first.
Last reviewed by Duncan Rogoff on November 7, 2026